Tuesday, 4 January 2011

How to Remove Palladium Pro (Uninstall Guide)

Palladium Pro is a rogue security program that pretends to be legitimate antivirus software and attempts to deceive unsuspecting PC users into paying to remove fake or simulated malware infections. Palladium Pro is a rebranded version of ThinkPoint rogue. It relies on social engineering, whereby the user is tricked into installing Trojan virus which masquerades as Microsoft Security Essentials and displays a fake security warning that uses the same fonts, colors, and layout as trusted security program. It makes false claims about having detected unknown Win32/Trojan and states that Microsoft Security Center has detected the submitted suspicious file as Trojan.Horse.Win32.PAV.64.a. Trojan then prompts the user to install Palladium Pro to solve the problem. As you may already know, profit is a primary motivation for creators of such malware. Please do not purchase Palladium Pro for any reason. If you are reading this article then your computer is probably infected with this fake program. Thankfully, we've got the removal instructions to help you to remove Palladium Pro and related malware from your computer. Please follow the removal guide below.


Thanks to rogueamp for making this video.

When you press the OK button, to allow Palladium Pro to install, the Trojan will reboot your computer to finish the installation.


After a reboot, you will see the "Palladium World's leading security solution" screen instead of your normal Windows desktop.


When you click the "Safe startup" button, the fake Palladium Pro scanner window will show up on your computer screen. The rogue will pretend to scan your computer for malware. After the fake scan, it will prompt you to buy heuristic modules to remove the threats from your computer which don't even exist. Do not fall victim to this rogue program. Furthermore, Palladium Pro will interfere with the normal operation of the computer. It will prevent you from launching other applications and block access to legitimate websites. In order to remove Palladium Pro from your computer, you will have to end its process, restore Windows explorer and scan your computer with anti-malware software. If you choose to remove the rogue program manually then you will also have to change Windows shell value in the registry; otherwise your Windows desktop will not be displayed the next time you reboot. Be advised, that the rogue may come bundled with other malicious software. That's why we strongly recommend you to use anti-malware software. For more information, please follow the removal instructions below. And, of course, if you have already purchased this bogus program, then you should contact your credit card company and dispute the charges. If you have any questions regarding Palladium Pro removal, then please leave a comment. Helpful comments are welcome as always. Good luck and be safe online!


Palladium Pro removal instructions:

1. Restart your computer. Once the "Palladium World's leading security solution" window comes press Ctrl+Alt+Delete or Ctrl+Shift+Escape. You should now see the Windows Task Manager screen as shown in the image below or a screen where you can select the Task Manager to be run.


Click on the Processes tab. Then click and highlight palladium.exe and click End Task. If it asks you "Are you sure you want to terminate the process?" click yes (or press Enter). This will close the ThinkPoint program.

2. While in Windows Task Manager, click the File -> "New Task (Run...)" from the menu on the bottom right. Type in explorer.exe and click OK. Your desktop and icons should start up as normal.


NOTE: if you got an error message "Windows cannot access the specified device, path or file. You may not have the appropriate permissions to access them", then please run this command first:

cacls "C:\Windows\explorer.exe" /G Everyone:F


A new windows will come up asking "Are you sure?" Type Y and press enter.


Now run explorer.exe again.

3. Download the following file to your Desktop: windows-shell.reg. Double-click to run it. Click "Yes" when it asks if you want to add the information to the registry. This file will fix the Windows Shell entry. This step is  important because if you won't fix this entry, then your Windows Desktop will not be displayed the next time you reboot. Once the new registry value has been added, you can delete the file from your computer.

4. Run Internet Explorer or any other browser and download free anti-malware software from the list below:
Run a full system scan and remove Palladium Pro from your computer.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator.

5. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET NOD32 Antivirus 4.


Palladium Pro associated files and registry values:

Files:

For Windows XP users:
  • C:\Documents and Settings\[User Name]\Application Data\palladium.exe
  • C:\Documents and Settings\[User Name]\Application Data\[SET OF RANDOM CHARACTERS].bat
  • C:\Documents and Settings\[User Name]\Application Data\uid_pal
  • C:\Documents and Settings\[User Name]\Application Data\completescan_pal
  • C:\Documents and Settings\[User Name]\Application Data\install_pal
  • C:\Documents and Settings\[User Name]\Desktop\Palladium.lnk
  • C:\Documents and Settings\[User Name]\Start Menu\Programs\Palladium.lnk
  • C:\Windows\Tasks\At[random].job
For Windows Vista and Windows 7 users:
  • C:\Users\[User Name]\AppData\Roaming\palladium.exe
  • C:\Users\[User Name]\AppData\Roaming\[SET OF RANDOM CHARACTERS].bat
  • C:\Users\[User Name]\AppData\Roaming\uid_pal
  • C:\Users\[User Name]\AppData\Roaming\completescan_pal
  • C:\Users\[User Name]\AppData\Roaming\install_pal
  • C:\Users\[User Name]\Desktop\Palladium.lnk
  • C:\Users\[User Name]\Start Menu\Programs\Palladium.lnk
  • C:\Windows\Tasks\At[random].job
Registry values:
  • HKEY_CURRENT_USER\Software\Microsoft\Windows NT\CurrentVersion\Winlogon "Shell = "%AppData%\palladium.exe"
Share this information with other people:

Monday, 3 January 2011

How to Remove Protect Shield (Uninstall Guide)

Protect Shield is a piece of malware classified as rogue a rogue antivirus program. This rogue doesn't mimic existing legitimate security software but I'm sure it may fool potential victims into paying for this bogus program which actually provides a user with little or no protection. Protect Shield can be manually installed by the user when he or she opens an attachment or visits a malicious website designed to automatically download and install rogue applications. The rogue program then pretends to scan your computer for malware and reports false scan results to make you think that your computer in infected with adware, spyware, trojans and other malicious software. Furthermore, Protect Shield displays fake claims of threats, even if your computer has not been compromised. It gives a false sense of security and may actually expose a computer to additional threats.


When Protect Shield is running, it may prevent your computer from accessing legitimate security vendor websites. It may hijack Internet Explorer and other web browsers and redirect you to unrelated websites full of ads and malicious code. This scareware displays a fake Windows Security Center pop-up saying that your computer is not protected and that you should install anti-virus software to remove the threats and protect your computer against viruses. The fake security warnings from your Windows task bar may state that your computer is under attack from a remote server and that your sensitive information can be stolen. Of course, that's not true. However, the personal and credit card information that you provide if you register this fake program could be used in additional fraud. That's why you shouldn't purchase Protect Shield for any reason. If you have already purchased it, then please contact your credit card company and dispute the charges stating that Protect Shield is a computer infection. If you have this rogue program on your computer, please follow the removal instructions below to remove Protect Shield and any related malware for free using legitimate anti-malware software. If you have any questions, please leave a comment. Good luck and be safe online!


Protect Shield removal instructions:

1. Download Process Explorer. (click the link and wait for few seconds, download will begin automatically)
2. End Protect Shield process: ProtectShield.exe
3. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Protect Shield removal instructions (in Safe Mode with Networking):

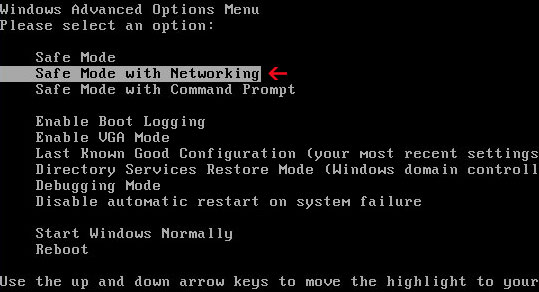
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Protect Shield associated files and registry values:

Files:
  • C:\Documents and Settings\All Users\Desktop\ProtectShield.lnk
  • C:\Documents and Settings\All Users\Start Menu\Programs\ProtectShield\
  • C:\Documents and Settings\All Users\Start Menu\Programs\ProtectShield\1 ProtectShield.lnk
  • C:\Documents and Settings\All Users\Start Menu\Programs\ProtectShield\2 Homepage.lnk
  • C:\Documents and Settings\All Users\Start Menu\Programs\ProtectShield\3 Uninstall.lnk
  • C:\Program Files\ProtectShield\
  • C:\Program Files\ProtectShield\license.txt
  • C:\Program Files\ProtectShield\ProtectShield.exe
  • C:\Program Files\ProtectShield\uninstall.exe
Registry values:
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\ProtectShield
  • HKEY_LOCAL_MACHINE\SOFTWARE\ProtectShield
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "ProtectShield"
Share this information with other people:

Remove Guardpe.com

Guardpe.com is a misleading website that promotes a rogue security program called Antivirus Scan. Normally, you wouldn't visit such websites but if you got hit with the Antivirus Scan malware then you will be constantly redirected to Guardpe.com instead of the requested web page. A new Internet Explorer window may pop up like every one or two minutes saying that you need to purchase Antivirus Scan in order to remove the infections and to protect your computer against new threats. Please do not buy anything from Guardpe.com. If you have Antivirus Scan malware on your computer, please follow the Antivirus Scan removal guide.

A screenshot of Guardpe.com:

How to Remove HDD Fix (Uninstall Guide)

HDD Fix is a form of computer malware that pretends to be a legitimate disk defragmenter. It misleads users into paying for the simulated removal of hard drive and Windows registry errors. It gives a false sense of security and actually provides you with no protection whatsoever. After the installation, HDD Fix will write itself into start-up of the operating system. It will imitate computer scan and report numerous critical hard drive errors. The rogue program will offer to fix supposedly detected errors once you purchase the license for this malware. HDD Fix is a typical rip-off rogue. It goes without saying that you shouldn't purchase it. If you have this rogue program on your computer then please follow the removal instructions below to remove HDD Fix and any related malware from your computer for free using legitimate anti-malware software.


HDD Fix is a rebranded version of HDD Low and Quick Defrag scareware. This rogue is promoted via trojans and misleading or infected websites. When running, it will block nearly all programs on your computer. If you attempt to launch a program, e.g. malware removal tool, it will terminate it and state that the program or hard drive is corrupted.
Windows detected a hard drive problem.
A hard drive error occurred while starting the application.


NOTE: you can rename the executable of your program to iexplore.exe and the rogue program shouldn't block it. Let's say you have the setup file of MalwareBytes' Antimalware (mbam-setup.exe) and the rogue program blocks it. Just rename mbam-setup.exe to iexplore.exe. This should do the trick. This method works with other programs too.

It will display fake notifications and alerts from Windows task bar.
Critical Error
Windows can't find hard disk space. Hard drive error


Application Data directory in Windows XP containing HDD Fix files:


C:\Documents and Settings\All Users\Application Data, by default this directiry is hidden. Please read Show Hidden Files and Folders in Windows for more information.

As you can see, this rogue uses random file names. It loads two executable files and one dll file. If you rename these files, the rogue program won't show up after the next reboot. However, HDD Fix may come bundled with rootkits, e.g. from the TDSS family. That's why you need to use anti-malware software to completely remove HDD Fix and related malware from your computer. For more information, please follow the steps in the removal guide below. Last, but not least, if you have already purchased this bogus program then you should contact your credit card and dispute the charges. If you have any questions or additional information about HDD Fix, please leave a comment. Good luck and be safe online!


HDD Fix removal instructions:

1. Download Process Explorer. (click the link and wait for few seconds, download will begin automatically)
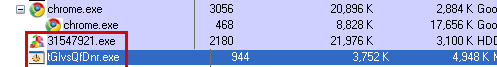
2. End HDD Fix processes, e.g. uleQbwvOIFTarei.exe or eyYndJAS.exe.


3. Download TDSSKiller (free utility from Kaspersky Lab) and run it. Remove TDSS rootkit if exist.


4. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

5. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


HDD Fix removal instructions (in Safe Mode with Networking):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


HDD Fix associated files and registry values:

Files:
  • %AppData%\[SET OF RANDOM CHARACTERS]
  • %AppData%\[SET OF RANDOM CHARACTERS].exe
  • %AppData%\dfrg
  • %AppData%\dfrgr
  • %AppData%\[SET OF RANDOM CHARACTERS].dll
  • %UserProfile%\Desktop\HDD Fix.lnk.lnk
  • %UserProfile%\Start Menu\Programs\HDD Fix.lnk\
  • %UserProfile%\Start Menu\Programs\HDD Fix\HDD Fix.lnk
  • %UserProfile%\Start Menu\Programs\HDD Fix\Uninstall HDD Fix.lnk
%AppData% refers to:
C:\Documents and Settings\All Users\Application Data (in Windows 2000/XP)
C:\Users\[UserName]\AppData\Roaming (in Windows Vista & Windows 7)

%UserProfile% refers to:
C:\Documents and Settings\[UserName]\ (in Windows 2000/XP)
C:\Users\[UserName]\ (in Windows Vista & Windows 7)

Registry values:
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS]"
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS].exe"
Share this information with other people:

Sunday, 2 January 2011

Remove Adware.StartPage (Uninstall Guide)

Adware.StartPage pretends to be a valid program but actually it is an adware that modifies the Internet Explorer home page without the user's permission. This adware changes certain Windows registry values so that it starts automatically when the user logins to Windows. It may modify Windows Hosts file and add a list of URLs to the Favorites folder, some of which may contain adult content as well. Basically, Adware.StartPage is designed to deliver various advertisements to the users' systems. I'm sure you know how to change the home page in Internet Explorer. Unfortunately, Adware.StartPage changes Internet Explorer's behavior, so you won't be able to change your home page through Internet Explorer settings as you would normally do. To remove Adware.StartPage from your computer, please follow the removal instructions below.

Alias: Trojan.Win32.StartPage.agxj [Kaspersky Lab]

Here's an example of the modified home page in Internet Explorer: tt265(dot)net.


Adware.StartPage removal instructions:

1. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

2. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Adware.StartPage associated files and registry values:

Files:
  • C:\Documents and Settings\All Users\Desktop\Internat Explorar.oc
  • C:\Documents and Settings\[UserName]\Local Settings\Temp\temp_tmp.bat
  • C:\Program Files\Microsoft\Internat Explorer\Desktop.ini
  • C:\Program Files\Microsoft\Internat Explorer\target.lnk
  • C:\Windows\System32\winproc32.exe
Registry values:
  • HKEY_LOCAL_MACHINE\SOFTWARE\Classes\.oc "ocfile"
  • HKEY_LOCAL_MACHINE\SOFTWARE\Classes\ocfile
  • HKEY_LOCAL_MACHINE\SOFTWARE\Classes\ocfile\DefaultIcon "%1"
  • HKEY_LOCAL_MACHINE\SOFTWARE\Classes\ocfile\shell
  • HKEY_LOCAL_MACHINE\SOFTWARE\Classes\ocfile\shell\open
  • HKEY_LOCAL_MACHINE\SOFTWARE\Classes\ocfile\shell\open\command "explorer "%ProgramFiles%\Microsoft\Internat Explorer"
Share this information with other people:

How to Remove Quick Defrag (Uninstall Guide)

Quick Defrag is a rogue hard disk defragmentation program that uses fraudulent scanner and fake error messages to make you think that your hard disk is experiencing critical errors. Usually, such rogue programs are often rebranded or cloned versions of previously developed programs. In this case, Quick Defrag is a clone of Quick Defragmenter and HDD Low malware. This rogue program is unknowingly installed onto a computer when a user visits a malicious website designed to automatically download and install malicious software. Once installed, Quick Defrag pretends to scan your computer for errors and malcode. Then it displays fake claims of hard disk errors and Windows registry problems even if your computer has not been compromised. Quick Defrag uses continuous pop-up displays, taskbar notification icons, and other alerts to indicate that you need to purchase a full version of the program in order to remove the reported threats and clean the computer. If you have this fake scanner on your computer then please follow the removal instructions below to remove Quick Defrag and related malware for free using legitimate anti-malware software.

While Quick Defrag is running, it will make it so you cannot run any programs on your computer. It will block task manager and other tools too telling you that your hard drive is corrupted. The fake error message that you will see when you attempt to run a program is:
Windows detected a hard drive problem.
A hard drive error occurred while starting the application.
It will also display fake notifications from your task bar.
Critical Error
Hard Drive not found. Missing hard drive.
Critical Error
RAM memory usage is critically high. RAM memory failure.
Critical Error
A critical error has occurred while indexing data stored on hard drive. System restart required.
As you can see, Quick Defrag is a typical rip-off rogue application. If you have already purchased it then you should contact your credit card company and dispute the charges because QuickDefrag is a scam. Be advised, that this rogue program can come bundled with other malicious software, adware, rootkits, etc. In order to completely remove Quick Defrag from your computer, please follow the steps in the removal guide below. If you've got any further questions about this fake scanner, please leave a comment below. Good luck and be safe online!


Quick Defrag removal instructions:

1. Open Task Manager (Ctrl+Alt+Delete) or use Process Explorer.
2. Click on the Processes tab.
3. End Quick Defrag process, e.g. tGldgRksm.exe or 1584321.exe.


4. Download TDSSKiller (free utility from Kaspersky Lab) and run it. Remove TDSS rootkit if exist.


5. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

6. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Quick Defrag removal instructions (in Safe Mode with Networking):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Quick Defrag associated files and registry values:

Files:
  • %Temp%\[SET OF RANDOM CHARACTERS].exe
  • %Temp%\dfrg
  • %Temp%\dfrgr
  • %Temp%\[SET OF RANDOM CHARACTERS].dll
  • %UserProfile%\Desktop\Quick Defrag.lnk
  • %UserProfile%\Start Menu\Programs\Quick Defrag\
  • %UserProfile%\Start Menu\Programs\Quick Defrag\Quick Defrag.lnk
  • %UserProfile%\Start Menu\Programs\Quick Defrag\Uninstall Quick Defrag.lnk
%Temp% refers to:
C:\Documents and Settings\[UserName]\Local Settings\Temp (in Windows 2000/XP)
C:\Users\[UserName]\AppData\Local\Temp (in Windows Vista & Windows 7)

%UserProfile% refers to:
C:\Documents and Settings\[UserName]\ (in Windows 2000/XP)
C:\Users\[UserName]\ (in Windows Vista & Windows 7)

Registry values:
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS]"
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS].exe"
Share this information with other people:

Saturday, 1 January 2011

Show Hidden Files and Folders in Windows

By default Microsoft Windows hides important files from being seen with Windows Explorer in order to protect these files from being modified or deleted by the user. Unfortunately viruses, rogue programs and other type of malicious software may hide files making it hard to find and delete them. Please follow the step-by-step directions below to show all hidden files in Windows.

Table of Contents:


Windows XP

1. Go to Start → Control Panel and choose Folder Options.


2. Double-click on the Folder Options icon. Click on the View tab.


3. Under the Hidden files and folders section, click Show hidden files and folders, and remove the checkmark from the checkbox labeled Hide protected operating system files. Click OK.


Windows Vista

1. Click on the Start button and then click on the Control Panel menu option.


2. In Control Panel, click Appearance and Personalization, and then click Folder Options.


3. Click the View tab. Under the Hidden files and folders section, click Show hidden files and folders, and remove the checkmark from the checkbox labeled Hide protected operating system files. Click OK.


Windows 7

1. Click on the Start button, then type in "folder options" into the search box. You will now see the search results. Just click on the Folder Options to open it.


2. Under the Hidden files and folders section, click Show hidden files, folders, and drives. Then remove the checkmark from the checkbox labeled Hide protected operating system files. Click OK.


Now your computer is configured to show all hidden files and folders. Hidden files will appear as if they are faint (slightly grayed out).