Share this information with other people:
Friday, 16 July 2010
Remove antiviractive.net (Free Removal)
As you remember, two days ago we wrote about antiviractive.com which is a rogue website related to Antivir Solution Pro malware. Today, we want to inform you about antiviractive.net. It's yet another misleading website that promotes the rogue program. If you are being constantly redirected to antiviractive.net then your computer is infected with Antivir Solution Pro or Trojan Horses that promote the rogue program. It goes without saying that you should remove the rogue program and additional malware from your computer as soon as possible. Also note that it can download more malware onto your computer. Removal delay will only worsen your situation. For more information please read this article on how to remove Antivir Solution Pro fro free. If you have any questions about this virus please don't hesitate and leave a comment. Good luck and be safe!

Share this information with other people:
Thursday, 15 July 2010
Remove webantispy.com and webantispy.net (Free Removal)
Today we came up with two misleading websites that promote the rogue anti-virus program called Antivir Solution Pro — webantispy.com and webantispy.net. You should block these domains using your antivirus or firewall software. And of course, you shouldn't visit them. Why? The answer is simple. Because both websites provide false information and "pushes" their bogus software. As you can see, webantispy.com just like webantispy.net uses the same web template. In fact, the same web template was used for antiviractive.com and several other rogue websites. We can say that malware creators are a bit lazy at this point.
Anyway, if you find that your computer is infected with AntivirSolutionPro scareware or you are being constantly redirected to webantispy.com or webantispy.net then please follow Antivir Solution Pro removal guide. Also note that you may have to use two or more malware removal tools to completely remove this virus and addition malware from your computer. Most importantly, don't purchase the rogue program. If you have any questions or additional information about this malware please leave a comment. Good luck and be safe!

Share this information with other people:
Anyway, if you find that your computer is infected with AntivirSolutionPro scareware or you are being constantly redirected to webantispy.com or webantispy.net then please follow Antivir Solution Pro removal guide. Also note that you may have to use two or more malware removal tools to completely remove this virus and addition malware from your computer. Most importantly, don't purchase the rogue program. If you have any questions or additional information about this malware please leave a comment. Good luck and be safe!
Share this information with other people:
Wednesday, 14 July 2010
Remove antiviractive.com (Free Removal)
Antiviractive.com is a rogue website that promotes Antivir Solution Pro which is a fake anti-virus program. Basically, it's a pay page of the rogue program. Once your computer is infected with the rogue program you will be constantly redirect to Antiviractive.com. The misleading website is full of false information, reviews, comments and etc. Please note that there are probably many more rogue websites that promote Antivir Solution Pro malware. Antiviractive.com is only one of them.
If you find that your computer is infected with Antivir Solution Pro scareware or you are being constantly redirected to Antiviractive.com without any particular reason please follow Antivir Solution Pro removal instructions. After you remove the rogue program and any related malware from your computer, please make sure to use an anti-malware or anti-virus program with a solid real time protection. Our favorite anti-virus program is ESET NOD32. Good luck and be safe!

Share this information with other people:
If you find that your computer is infected with Antivir Solution Pro scareware or you are being constantly redirected to Antiviractive.com without any particular reason please follow Antivir Solution Pro removal instructions. After you remove the rogue program and any related malware from your computer, please make sure to use an anti-malware or anti-virus program with a solid real time protection. Our favorite anti-virus program is ESET NOD32. Good luck and be safe!
Share this information with other people:
Tuesday, 13 July 2010
How to remove Antivir Solution Pro (Uninstall Instructions)
Antivir Solution Pro is a fake anti-virus program. It reports false infections or system security threats on your computer and then prompts you to pay for a full version of the program to remove the threats. This rogue program must be manually installed, but very often users state that it comes like from nowhere and that they didn't install it. Please note that Antivir Solution Pro is promoted mainly through the use of Trojans. Trojan Horses may enter your computer through software vulnerabilities and then later download the rogue program onto your computer. Also, malware creators use social engineering to distribute their bogus software. One way or another, if you are reading this article then your computer is probably infected with AntivirSolutionPro malware. The good news is that you can remove Antivir Solution Pro from your computer for free using legitimate anti-malware programs. Please follow the removal instructions below.

This fake program is from the same family as AV Security Suite and Antivirus Soft scareware. The most annoying thing about Antivir Solution malware is that it actually blocks legitimate anti-virus and anti-malware programs. It also disables system tools and utilities such as Task Manager, Registry Editor and System restore. Antivir Solution Pro hijacks web browsers too. Some users might not be able to use Google search or look for any other assistance on the Internet. The rogue program configures Windows to use a proxy server. It intercepts the request and display fake security warnings or misleading websites that promote Antivir Solution Pro. What is more, the rogue program may redirect you to adult websites. The fake Internet Explorer alert reads:
"Internet Explorer Warning - visiting this web site may harm your computer!".

Other fake alerts:
"Windows Security alert
Application cannot be executed. The file notepad.exe is infected.
Do you want to active your antivirus software now?"

"Antvirus software alert
Infiltration alert - Virus attack
Your computer is being attacked by internet virus. It could be a password stealing attack, a trojan - dropper or similar.
Threat: Win32/Nuqel.E
Threat: BankerFox.A"
Screensot of antiviractive.net

As you can see, this rogue program has only one purpose — to scare you into purchasing it. It's absolutely needless and even dangerous program. We strongly recommend you to remove Antivir Solution Pro from your computer as soon as possible. If you have already paid for it then contact your credit card company and dispute the charges. Finally, please follow the removal instructions below and don’t hesitate to leave a comment if you have any questions or additional information about this virus. Good luck and be safe!
Antivir Solution Pro removal instructions (in Safe Mode with Networking):
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm

NOTE: Login as the same user you were previously logged in with in the normal Windows mode.
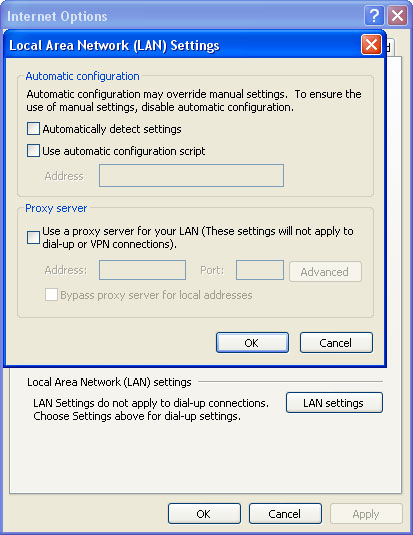
2. Launch Internet Explorer. In Internet Explorer go to: Tools->Internet Options->Connections tab.
Click Lan Settings button and uncheck the checkbox labeled Use a proxy server for your LAN. Click OK.

3. Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.
Alternative Antivir Solution Pro removal instructions using HijackThis (in Normal mode):
1. Download iexplore.exe (NOTE: iexplore.exe file is renamed HijackThis tool from TrendMicro).
Launch the iexplore.exe and click "Do a system scan only" button.
If you can't open iexplore.exe file then download explorer.scr and run it.
2. Search for similar entries in the scan results:
R1 – HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = http=127.0.0.1
O4 – HKLM\..\Run: [ortplkfr] C:\Documents and Settings\[User]\Local settings\Application data\jgrpldf\rftpldtssd.exe
O4 – HKCU\..\Run: [ortplkfr] C:\Documents and Settings\[User]\Local settings\Application data\jgrpldf\rftpldtssd.exe
The process name will be different in your case [SET OF RANDOM CHARACTERS]tssd.exe, located in C:\Documents and Settings\[UserName]\Local settings\Application data\
Select all similar entries and click once on the "Fix checked" button. Close HijackThis tool.
3. Delete the follow file C:\WINDOWS\Prefetch\[RANDOM]TSSD.EXE-[RANDOM].pf
4. Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
Antivir Solution Pro associated files and registry values:
Files:
This fake program is from the same family as AV Security Suite and Antivirus Soft scareware. The most annoying thing about Antivir Solution malware is that it actually blocks legitimate anti-virus and anti-malware programs. It also disables system tools and utilities such as Task Manager, Registry Editor and System restore. Antivir Solution Pro hijacks web browsers too. Some users might not be able to use Google search or look for any other assistance on the Internet. The rogue program configures Windows to use a proxy server. It intercepts the request and display fake security warnings or misleading websites that promote Antivir Solution Pro. What is more, the rogue program may redirect you to adult websites. The fake Internet Explorer alert reads:
"Internet Explorer Warning - visiting this web site may harm your computer!".
Other fake alerts:
"Windows Security alert
Application cannot be executed. The file notepad.exe is infected.
Do you want to active your antivirus software now?"
"Antvirus software alert
Infiltration alert - Virus attack
Your computer is being attacked by internet virus. It could be a password stealing attack, a trojan - dropper or similar.
Threat: Win32/Nuqel.E
Threat: BankerFox.A"
Screensot of antiviractive.net
As you can see, this rogue program has only one purpose — to scare you into purchasing it. It's absolutely needless and even dangerous program. We strongly recommend you to remove Antivir Solution Pro from your computer as soon as possible. If you have already paid for it then contact your credit card company and dispute the charges. Finally, please follow the removal instructions below and don’t hesitate to leave a comment if you have any questions or additional information about this virus. Good luck and be safe!
Antivir Solution Pro removal instructions (in Safe Mode with Networking):
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm

NOTE: Login as the same user you were previously logged in with in the normal Windows mode.
2. Launch Internet Explorer. In Internet Explorer go to: Tools->Internet Options->Connections tab.
Click Lan Settings button and uncheck the checkbox labeled Use a proxy server for your LAN. Click OK.
3. Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.
Alternative Antivir Solution Pro removal instructions using HijackThis (in Normal mode):
1. Download iexplore.exe (NOTE: iexplore.exe file is renamed HijackThis tool from TrendMicro).
Launch the iexplore.exe and click "Do a system scan only" button.
If you can't open iexplore.exe file then download explorer.scr and run it.
2. Search for similar entries in the scan results:
R1 – HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = http=127.0.0.1
O4 – HKLM\..\Run: [ortplkfr] C:\Documents and Settings\[User]\Local settings\Application data\jgrpldf\rftpldtssd.exe
O4 – HKCU\..\Run: [ortplkfr] C:\Documents and Settings\[User]\Local settings\Application data\jgrpldf\rftpldtssd.exe
The process name will be different in your case [SET OF RANDOM CHARACTERS]tssd.exe, located in C:\Documents and Settings\[UserName]\Local settings\Application data\
Select all similar entries and click once on the "Fix checked" button. Close HijackThis tool.
3. Delete the follow file C:\WINDOWS\Prefetch\[RANDOM]TSSD.EXE-[RANDOM].pf
4. Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
Antivir Solution Pro associated files and registry values:
Files:
- %UserProfile%\Local Settings\Application Data\[SET OF RANDOM CHARACTERS]\
- %UserProfile%\Local Settings\Application Data\[SET OF RANDOM CHARACTERS]\[SET OF RANDOM CHARACTERS]tssd.exe
- C:\Users\User\AppData\Local\[SET OF RANDOM CHARACTERS] (Windows Vista & Windows 7)
- C:\WINDOWS\Prefetch\[RANDOM]TSSD.EXE-[RANDOM].pf
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run\"[RANDOM CHARACTERS]" = "%UserProfile%\Local Settings\Application Data\[SET OF RANDOM CHARACTERS]\[SET OF RANDOM CHARACTERS]tssd.exe"
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run\"[RANDOM CHARACTERS]" = "%UserProfile%\Local Settings\Application Data\[SET OF RANDOM CHARACTERS]\[SET OF RANDOM CHARACTERS]tssd.exe"
- HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Download\"CheckExeSignatures" = "no"
- HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Download\"RunInvalidSignatures" = "1"
- HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\PhishingFilter\"EnabledV8" = "0"
- HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\PhishingFilter\"Enabled" = "0"
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Policies\Attachments\"SaveZoneInformation" = "1"
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Policies\Associations\"LowRiskFileTypes" = ".exe"
- HKEY_LOCAL_MACHINE\SOFTWARE\AVSuitE
- HKEY_LOCAL_MACHINE\SOFTWARE\avSofT
- HKEY_CURRENT_USER\Software\avSofT
Saturday, 10 July 2010
Remove Antispyware Defender scam (Uninstall Instructions)
Today we came across another rogue domain — antispy-defender.com. This time malware authors "pushes" a new rogue program called Antispyware Defender. If your computer got infected with Antispyware Defender or you are being constantly redirect to antispy-defender.com or any other unrelated websites, please scan your PC with legitimate anti-malware software. Detailed removal instructions will be added as soon as they become available. Meanwhile, please note that Antispyware Defender is not a legitimate program and antispy-defender.com is rogue domain. Don't purchase AntispywareDefender. If you have already paid for it then please contact your credit card company and dispute the charges. Good luck and be safe!
Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe.With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
Screenshot of antispy-defender.com

Share this information with other people:
Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe.With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
Screenshot of antispy-defender.com
Share this information with other people:
AntivirusGT removal instructions (Uninstall Guide)
AntivirusGT is one of many fake anti-virus programs that report fake viruses and prompt you to pay for a full version of the program to remove the infections or viruses which don't even exist. This fake program prevents users from doing most things. It blocks Task Manager, Registry editor, legitimate anti-virus and anti-malware programs or other useful system utilities. AntivirusGT also gives you loads of fake security warnings and pop-ups. Those fake warnings claim that your computer is infected with spyware, adware, Trojans, computer worms and other viruses. Antivirus GT performs a very quick scan and displays a list of non-existent infections. If you are reading this article, then your computer is probably infected with this virus and you're looking for removal help. Thankfully, we've got free AntivirusGT removal instructions to help you get rid of this malicious software.

Please note that such fake programs usually come from fake anti-malware scanners, misleading online video websites and other bogus pages. AntivirusGT virus may come bundled with other malware as well. In some cases the rogue program has to be manually installed, but it usually pretends to be a legitimate program such as flash player, video codec or any other application. While running, the rogue program blocks nearly all legit programs and displays an error message with the following text (process name may vary):
AntivirusGT Resident Shield: Virus Detected
Warning! Active virus detected!
Threat Detected: Trojan.Injector.BZ
Infected File: C:\Windows\System32\rundll32.exe

What is more, AntivirusGT hijacks Internet Explorer and Mozilla Firefox, adds malicious browser helper object and displays fake security warning every time you attempt to visit security related websites. The text of this alert is:
Attention! Your web page request has been cancelled.
This web site refused your connection as it was reported as a malicious request. This can be caused by Viruses, Trojans or Malware installed on your computer.

Antivirus GT is from the same family as Antivirus 7 malware. It goes without saying that AntivirusGT is needless and potentially harmful software. Also, note that malware authors constantly changes code of such rogue programs to avoid detection and to maximize their return of investment. Most importantly, don't purchase this rogue program. If you have already paid for it then you should contact your credit card company and dispute the charges. Finally, please follow the removal instructions below to remove AntivirusGT from your computer for free using legitimate anti-malware programs. And last, but not least, if you have any questions or additional information about this malware, please don't hesitate and leave a comment. Good luck and be safe!
AntivirusGT removal instructions (method #1):
1. (Proceed to step 2 if you your web browser is not hijacked) Open Internet Explorer. Go to: Tools->Manage Add-ons. Find and select UpdateCheck.dll from the list of add-ons. Click "Disable" button and close Manager Add-ons windows. Close Internet Explorer and run it once again.
2. Right click on Windows Task Bar, select Task Manager (or press Ctrl+Shift+Esc at the same time). Look for antivirusGT.exe process and terminate it (click End Process button).
3. Download one of the following legitimate anti-malware applications and run a quick system scan. Don’t forget to update it first. All programs a free.
NOTE1: If you can't run any of the above programs you must rename the installer of selected program before saving it on your PC. For example: if you choose MalwareBytes then you have to rename mbam-setup.exe to iexplore.exe, explorer.exe or any random name like test123.exe before saving it. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator.
NOTE2: if you still can't run the renamed file then you need to change file extension too not only the name.
1. Go to "My Computer".
2. Select "Tools" from menu and click "Folder Options".
3. Select "View" tab and uncheck the checkbox labeled "Hide file extensions for known file types". Click OK.
4. Rename mbam-setup.exe to either test123.com or test123.pif
5. Double-click to run renamed file.
Removing AntivirusGT in Safe Mode with Networking (method #2):
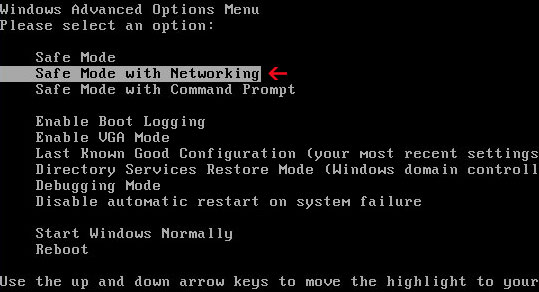
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm
NOTE: Login as the same user you were previously logged in with in the normal Windows mode.
2.Download one of the following legitimate anti-malware applications and run a quick system scan. Don’t forget to update it first. All programs a free.
AntivirusGT files and registry values:
Files:
Please note that such fake programs usually come from fake anti-malware scanners, misleading online video websites and other bogus pages. AntivirusGT virus may come bundled with other malware as well. In some cases the rogue program has to be manually installed, but it usually pretends to be a legitimate program such as flash player, video codec or any other application. While running, the rogue program blocks nearly all legit programs and displays an error message with the following text (process name may vary):
AntivirusGT Resident Shield: Virus Detected
Warning! Active virus detected!
Threat Detected: Trojan.Injector.BZ
Infected File: C:\Windows\System32\rundll32.exe
What is more, AntivirusGT hijacks Internet Explorer and Mozilla Firefox, adds malicious browser helper object and displays fake security warning every time you attempt to visit security related websites. The text of this alert is:
Attention! Your web page request has been cancelled.
This web site refused your connection as it was reported as a malicious request. This can be caused by Viruses, Trojans or Malware installed on your computer.
Antivirus GT is from the same family as Antivirus 7 malware. It goes without saying that AntivirusGT is needless and potentially harmful software. Also, note that malware authors constantly changes code of such rogue programs to avoid detection and to maximize their return of investment. Most importantly, don't purchase this rogue program. If you have already paid for it then you should contact your credit card company and dispute the charges. Finally, please follow the removal instructions below to remove AntivirusGT from your computer for free using legitimate anti-malware programs. And last, but not least, if you have any questions or additional information about this malware, please don't hesitate and leave a comment. Good luck and be safe!
AntivirusGT removal instructions (method #1):
1. (Proceed to step 2 if you your web browser is not hijacked) Open Internet Explorer. Go to: Tools->Manage Add-ons. Find and select UpdateCheck.dll from the list of add-ons. Click "Disable" button and close Manager Add-ons windows. Close Internet Explorer and run it once again.
2. Right click on Windows Task Bar, select Task Manager (or press Ctrl+Shift+Esc at the same time). Look for antivirusGT.exe process and terminate it (click End Process button).
3. Download one of the following legitimate anti-malware applications and run a quick system scan. Don’t forget to update it first. All programs a free.
NOTE1: If you can't run any of the above programs you must rename the installer of selected program before saving it on your PC. For example: if you choose MalwareBytes then you have to rename mbam-setup.exe to iexplore.exe, explorer.exe or any random name like test123.exe before saving it. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator.
NOTE2: if you still can't run the renamed file then you need to change file extension too not only the name.
1. Go to "My Computer".
2. Select "Tools" from menu and click "Folder Options".
3. Select "View" tab and uncheck the checkbox labeled "Hide file extensions for known file types". Click OK.
4. Rename mbam-setup.exe to either test123.com or test123.pif
5. Double-click to run renamed file.
Removing AntivirusGT in Safe Mode with Networking (method #2):
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm

NOTE: Login as the same user you were previously logged in with in the normal Windows mode.
2.Download one of the following legitimate anti-malware applications and run a quick system scan. Don’t forget to update it first. All programs a free.
AntivirusGT files and registry values:
Files:
- C:\Documents and Settings\All Users\Start Menu\AVGT\
- C:\Program Files\AVGT\
- C:\Program Files\AVGT\antivirusGT.exe
- %Temp%\MICROS~1.DLL
- HKEY_CURRENT_USER\Software\EVA246
- HKEY_CURRENT_USER\Software\WinFD
- HKEY_CLASSES_ROOT\CLSID\{3304F17F-732C-4AC6-BF67-DBDC8B88C11F}
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{3304F17F-732C-4AC6-BF67-DBDC8B88C11F}
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "AVGT"
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\User Agent\Post Platform "WinNT-EVI 05.07.2010"
Monday, 28 June 2010
How to remove Defense Center (Uninstall Instructions)
Defense Center is a typical fake anti-spyware program. It displays fake security warnings like every one or two minutes and states that your computer is infected with malware. Once installed, it will report numerous false system security threats. The rogue program may flag legitimate and safe Microsoft Windows files as Trojan Horses or other viruses. Don't attempt to remove those files. Otherwise your PC won't operate properly. As a typical rogue program Defense Center will prompt you to pay for a full version of the program to remove the infections which don't even exist. It goes without saying that you should remove Defense Center from your computer as soon as possible. Thankfully, we've got free Defense Center removal instructions to help you. Detailed removal guide is outlined below.

False scan results and fake security alerts shouldn't surprise you because DefenseCenter scareware will do all its best to trick you into purchase the program. It will even attempt to uninstall antivirus software from your computer. If you use let's say Norton Antivirus, then most likely you will see a fake pop-up claiming that your antivirus software is infected and should be uninstalled immediately. Defense Center will even block certain security related websites and block other useful utilities to protect itself from being removed. The text of some fake security alerts are:
"Warning! Virus threat detected!
Virus activity detected!
Net-Worm.Win32 has been detected. This adware module advertises websites with explicit content. Be advised of such content being possibly illegal. Please click the button below to locate and remove this threat."
"Danger!
A security threat detected on your computer. TrojanASPX.JS.Win32. It strongly recommended to remove this threat right now. Click on the message to remove it."
"Warning! Adware detected!
Adware module detected on your PC!
Zlob.Porn.Ad adware has been detected. This adware module advertises websites with explicit content. Be advised of such content being possibly illegal. Please click the button below to locate and remove this threat now."
Also note, that this rogue program is promoted mainly through the use of Trojan Horses. Very often Trojans download TDSS rootkit and other malware alongside Defense Center. That's why we think manual removal is not an options in this case. We strongly recommend you to run a full system scan with at least two anti-malware programs. Below you will find a list of free and reputable anti-malware programs which will remove Defense Center from your computer for good. By the way, if you have already purchased this bogus program, then please contact your credit card company and dispute the charges. Finally, if you have any questions about this virus, please don't hesitate and leave a comment.
Defense Center removal instructions (in Safe Mode with Networking, Method 1):
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm

NOTE: Login as the same user you were previously logged in with in the normal Windows mode.
2. Download SUPERAntispyware, MalwareBytes Anti-malware, Spybot - Search & Destroy or Spyware Doctor and run a full system scan. NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning. Then reboot your computer in "Normal Mode" and run a system scan again. That's it!
4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.
Defense Center removal instructions: (Method 2)
1. Download TDSSKiller.exe from Kaspersky website.
2. Execute the file TDSSKiller.exe (NOTE: you may have to rename TDSSKiller.exe to explorer.com yourself or download already renamed explorer.com file in order to run it)
3. Follow the prompts and wait for the scan and disinfection process to be over. Close all programs and press “Y” key to restart your computer.
More detail TDSSKiller tutorial: http://support.kaspersky.com/viruses/solutions?qid=208280684
4. Download one of the following anti-malware software and run a full system scan:
5. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.
Defense Center associated files and registry values:
Files:
False scan results and fake security alerts shouldn't surprise you because DefenseCenter scareware will do all its best to trick you into purchase the program. It will even attempt to uninstall antivirus software from your computer. If you use let's say Norton Antivirus, then most likely you will see a fake pop-up claiming that your antivirus software is infected and should be uninstalled immediately. Defense Center will even block certain security related websites and block other useful utilities to protect itself from being removed. The text of some fake security alerts are:
"Warning! Virus threat detected!
Virus activity detected!
Net-Worm.Win32 has been detected. This adware module advertises websites with explicit content. Be advised of such content being possibly illegal. Please click the button below to locate and remove this threat."
"Danger!
A security threat detected on your computer. TrojanASPX.JS.Win32. It strongly recommended to remove this threat right now. Click on the message to remove it."
"Warning! Adware detected!
Adware module detected on your PC!
Zlob.Porn.Ad adware has been detected. This adware module advertises websites with explicit content. Be advised of such content being possibly illegal. Please click the button below to locate and remove this threat now."
Also note, that this rogue program is promoted mainly through the use of Trojan Horses. Very often Trojans download TDSS rootkit and other malware alongside Defense Center. That's why we think manual removal is not an options in this case. We strongly recommend you to run a full system scan with at least two anti-malware programs. Below you will find a list of free and reputable anti-malware programs which will remove Defense Center from your computer for good. By the way, if you have already purchased this bogus program, then please contact your credit card company and dispute the charges. Finally, if you have any questions about this virus, please don't hesitate and leave a comment.
Defense Center removal instructions (in Safe Mode with Networking, Method 1):
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm

NOTE: Login as the same user you were previously logged in with in the normal Windows mode.
2. Download SUPERAntispyware, MalwareBytes Anti-malware, Spybot - Search & Destroy or Spyware Doctor and run a full system scan. NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning. Then reboot your computer in "Normal Mode" and run a system scan again. That's it!
4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.
Defense Center removal instructions: (Method 2)
1. Download TDSSKiller.exe from Kaspersky website.
2. Execute the file TDSSKiller.exe (NOTE: you may have to rename TDSSKiller.exe to explorer.com yourself or download already renamed explorer.com file in order to run it)
3. Follow the prompts and wait for the scan and disinfection process to be over. Close all programs and press “Y” key to restart your computer.
More detail TDSSKiller tutorial: http://support.kaspersky.com/viruses/solutions?qid=208280684
4. Download one of the following anti-malware software and run a full system scan:
5. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.
Defense Center associated files and registry values:
Files:
- C:\Program Files\Defense Center
- C:\Program Files\Defense Center\about.ico
- C:\Program Files\Defense Center\activate.ico
- C:\Program Files\Defense Center\buy.ico
- C:\Program Files\Defense Center\def.db
- C:\Program Files\Defense Center\defcnt.exe
- C:\Program Files\Defense Center\defext.dll
- C:\Program Files\Defense Center\defhook.dll
- C:\Program Files\Defense Center\help.ico
- C:\Program Files\Defense Center\scan.ico
- C:\Program Files\Defense Center\settings.ico
- C:\Program Files\Defense Center\splash.mp3
- C:\Program Files\Defense Center\Uninstall.exe
- C:\Program Files\Defense Center\update.ico
- C:\Program Files\Defense Center\virus.mp3
- %UserProfile%\Desktop\spam001.exe
- %UserProfile%\Desktop\spam003.exe
- %UserProfile%\Desktop\troj000.exe
- %UserProfile%\Desktop\youporn.com.lnk
- %UserProfile%\Start Menu\Programs\Defense Center
- HKEY_USERS\S-1-5-21-861567501-152049171-1708537768-1003_Classes\secfile
- HKEY_CURRENT_USER\Software\Classes\secfile
- HKEY_CLASSES_ROOT\CLSID\{5E2121EE-0300-11D4-8D3B-444553540000}
- HKEY_CLASSES_ROOT\secfile
- HKEY_LOCAL_MACHINE\SOFTWARE\Defense Center
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Defense Center
- HKEY_LOCAL_MACHINE\SOFTWARE\Program Groups
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Policies\System "DisableTaskMgr" = "1"
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "Defense Center"
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\system "DisableTaskMgr" = "1"
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Shell Extensions\Approved "{5E2121EE-0300-11D4-8D3B-444553540000}"
Subscribe to:
Posts (Atom)